
Project management (PM) platforms hold a lot of sensitive client data: contracts, budgets, schedules, files and the conversations around them. Yet many still let people sign in with a short, reused password and nothing else. For a project manager, that is not an IT detail. One weak login can expose a client, delay the project and damage the trust your team has built.
- Weak passwords are still everywhere: 65.8% of the 2 billion passwords leaked in 2025 had fewer than 12 characters, and only 3.2% had 16 or more.
- Enforced multi-factor authentication (MFA) is the control that matters most. CISA says MFA makes you 99% less likely to be hacked, and the Change Healthcare and Snowflake breaches both started with accounts that had no MFA.
- Password rules changed: NIST now asks for 15 characters when the password is the only factor, breached-password checks, no forced symbols and no 90-day resets.
- Project managers control more than they think: who gets access, how fast leavers are removed and which apps connect to the platform. The free PM Platform Security Scorecard below turns that into a fix list.
This guide explains why weak passwords are a project risk, what secure project management software should include in 2026, the steps a project manager can take today, and where online fraud insurance fits. Each section uses real incidents and current data, so you can make the case to your sponsor or your IT team.
The Risk of Weak Passwords
Weak passwords open the door to phishing, credential stuffing (trying passwords leaked from one site on another), data breaches and unauthorized access. For a project team, the result is concrete: a leaked client file, a schedule that slips while systems are locked, or a compliance problem the sponsor has to explain.
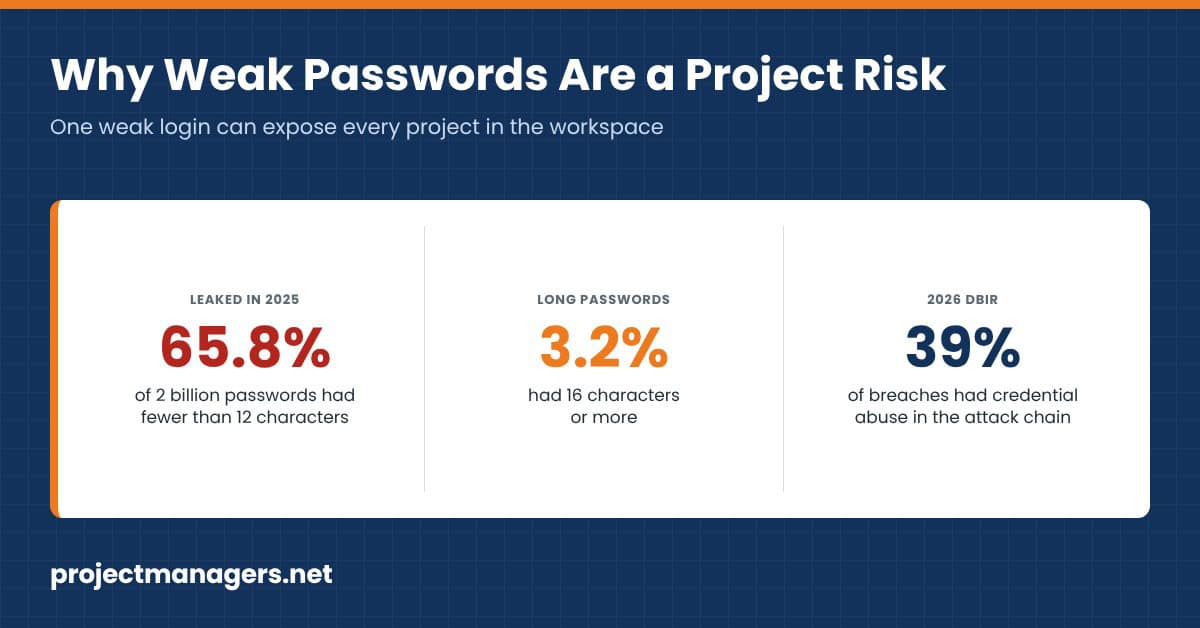
The numbers have not improved much. A Comparitech study of more than 2 billion passwords leaked in 2025 found that 65.8% had fewer than 12 characters and only 3.2% had 16 or more. Among the 1,000 most common passwords, 38.6% contained the string “123.” Demandsage counts 2.28 billion password-related leaks among 18.4 billion data points leaked in the United States, and reports that 84% of people reuse passwords.
Attackers do not need to crack anything when a password has already leaked. In Verizon’s 2026 Data Breach Investigations Report, exploited vulnerabilities passed stolen credentials as the most common way in, yet the Center for Internet Security notes that credential abuse still appeared somewhere in the attack chain of 39% of breaches. All it takes is one project team member with a weak or reused password, and every project in the workspace is exposed.
Real-life example
Snowflake 2024: about 165 organizations exposed with logins that were already stolen
In 2024, a criminal group signed in to the Snowflake accounts of about 165 customer organizations. Snowflake itself was not breached. The attackers used usernames and passwords stolen earlier by infostealer malware, some from as far back as 2020, and the accounts they used did not have MFA turned on. Mandiant found that at least 79.7% of those accounts had credentials exposed before the attack.
Source: Mandiant (Google Cloud), UNC5537 Targets Snowflake Customer Instances
For project managers: a cloud platform can be secure and still leak your data if your own accounts rely on a password alone. Check that MFA is enforced, not just available, in every tool that holds client data, including the ones a client or vendor manages for the project.
From the source
“Mandiant assesses MFA would have prevented compromise of Snowflake accounts in this campaign”
Austin Larsen, senior threat analyst at Mandiant, quoted by Dark Reading
By the numbers
- 65.8%of passwords leaked in 2025 had fewer than 12 characters.Comparitech
- 39%of breaches in the 2026 DBIR had credential abuse somewhere in the attack chain.Center for Internet Security
What Secure PM Software Should Include

The blame for weak passwords does not fall only on users. Many platforms still accept short passwords, never check them against breach lists and leave MFA optional. If your PM platform still accepts weak passwords, it is time to rethink the tools your project team uses. Here is what to look for.
Enforced Multi-Factor Authentication (MFA)
A strong password is the first line of defense. MFA is what saves you when that password leaks anyway. The Cybersecurity and Infrastructure Security Agency (CISA) says MFA makes you 99% less likely to be hacked, and a Microsoft Research study measured a 99.22% lower risk of account compromise for accounts using MFA. MFA combines two or more of these factors:
- Something you know: your password or PIN
- Something you have: a phone with an authenticator app, a passkey or a security key
- Something you are: a fingerprint or face scan that unlocks a passkey
- Somewhere you are: location or network checks the platform uses to flag unusual sign-ins
Two details matter for a project manager. First, MFA has to be enforced by an admin, not left as an option each user may skip. Second, not all MFA is equal: passkeys, security keys and authenticator apps resist phishing far better than codes sent by SMS, so require them at least for admins and anyone who approves payments.
Real-life example
Change Healthcare 2024: a stolen password on a remote access portal
In February 2024, attackers used stolen credentials to log in to a Change Healthcare Citrix remote access portal. The portal did not have MFA. Nine days later they deployed ransomware, and pharmacies and providers across the United States were disrupted for weeks. UnitedHealth Group’s policy required MFA on external systems, but this one portal had slipped through.
Source: TechCrunch, Change Healthcare hackers broke in using stolen credentials, and no MFA
For project managers: a policy is not a control until every system follows it. List every tool your project uses (PM platform, file sharing, remote access, client portals) and confirm MFA is enforced on each one.
From the source
“The portal did not have multifactor authentication”
Andrew Witty, UnitedHealth Group CEO, in written testimony reported by TechCrunch
By the numbers
- 99%less likely to be hacked when MFA is used, according to CISA.CISA
- 99.22%lower risk of account compromise with MFA in a Microsoft study of Azure AD accounts.Microsoft Research
Password Rules That Follow NIST
A good platform lets admins enforce password policies for the whole workspace. What those policies should say has changed. In 2025 the U.S. National Institute of Standards and Technology finalized NIST SP 800-63B-4, and several old habits are now on the “do not” list:
| Rule | Old habit | What NIST SP 800-63B-4 says |
|---|---|---|
| Minimum length | 8 characters | 15 characters when the password is the only factor, 8 when it is part of MFA |
| Character mix | Force an uppercase letter, a number and a symbol | No composition rules: length matters more than symbols |
| Expiry | Change every 60 or 90 days | No scheduled changes, but a forced change when there is evidence of compromise |
| Blocklist | Rarely checked | Every new password is checked against common, expected and compromised passwords |
| Long passphrases | Often cut off at 16 or 20 characters | Allow at least 64 characters, so passphrases and password managers work |
In practice, look for a platform that blocks names, common words and passwords already seen in breaches, accepts long passphrases and supports single sign-on (SSO), so your company identity provider applies the same rules and MFA everywhere. Calendar-based resets do more harm than good: people just add a number to the old password.
Data Encryption
Encryption turns readable data into something useless without the key. Your PM platform should encrypt data in transit (TLS 1.2 or later between the browser and the servers) and at rest (on the servers and in backups), so a stolen disk or backup file does not expose your project files. This matters most when the project handles client financial, legal or health information.
Ask the vendor to confirm both in writing and to share a current SOC 2 Type II report or ISO 27001 certificate. Keep in mind that encryption protects data from people without access. It does nothing against someone who signs in with a valid, stolen password, which is why encryption and MFA work together.
Regular Security Updates
A good PM platform ships security fixes quickly. With a cloud (SaaS) tool, the vendor patches for you, so check how fast it reports and fixes vulnerabilities. With a self-hosted tool, your team owns patching: critical security updates, especially for flaws already being exploited, should go in within days, while minor updates can follow your normal weekly or monthly schedule.
Keep a simple log of each update and confirm it was applied on every server. Delays are expensive: in the 2026 Verizon DBIR, exploited vulnerabilities became the most common way attackers got in, at 31% of breaches.
Real-life example
Atlassian Confluence 2023: a critical flaw that let outsiders create admin accounts
In October 2023, Atlassian disclosed CVE-2023-22515 in self-hosted Confluence Data Center and Server. The flaw let attackers create their own administrator accounts without signing in. It was exploited as a zero-day before the patch, and CISA, the FBI and MS-ISAC warned that exploitation would continue on servers that were not updated. Atlassian’s cloud sites were not affected.
Source: CISA advisory AA23-289A, Threat Actors Exploit Atlassian Confluence CVE-2023-22515
For project managers: if your team self-hosts Jira, Confluence or another project tool, subscribe to the vendor security advisories and treat a critical patch like a schedule-critical task with an owner and a deadline.
From the source
“expect widespread, continued exploitation due to ease of exploitation”
CISA, FBI and MS-ISAC joint advisory AA23-289A
By the numbers
- 1 dayafter disclosure, CISA added the flaw to its Known Exploited Vulnerabilities catalog (October 5, 2023).CISA
- 31%of breaches in the 2026 DBIR started with an exploited vulnerability, the top route in.Verizon DBIR
User Access Controls
User access controls are a critical line of defense in any project management platform. Even with strong passwords, loose permissions leave sensitive data exposed. Access controls decide who can view, edit, export or delete project information, and a badly configured role can let the wrong person in, by accident or on purpose.
Look for role-based permissions, guest accounts limited to specific projects, admin control over which apps and AI connectors can reach your data, and audit logs that show who exported what. Integrations are access too: every connected app, API token and AI assistant can read whatever its user can read.
Real-life example
Asana 2025: an AI connector bug exposed data across organizations
In May 2025, Asana launched a Model Context Protocol (MCP) server so AI assistants could work with Asana data. On June 4, it found a logic flaw that could expose information from one organization to MCP users at other organizations. Asana took the server offline from June 5 to June 17, fixed the code and notified customers who had used it. A spokesperson told BleepingComputer that about 1,000 customers were affected.
Source: BleepingComputer, Asana warns MCP AI feature exposed customer data to other orgs
For project managers: treat every new AI connector or integration as a new user with access to your project data. Approve it, limit it to the projects that need it and review it with your other accounts every quarter.
From the source
“could have potentially exposed certain information from your Asana domain to other Asana MCP users”
Asana customer notice, quoted by The Register
By the numbers
- ~1,000Asana customers were affected by the MCP data exposure bug.BleepingComputer
- 13 daysthe MCP server stayed offline (June 5 to June 17, 2025) while the flaw was fixed.The Register
Practical Steps Project Managers Can Take Today
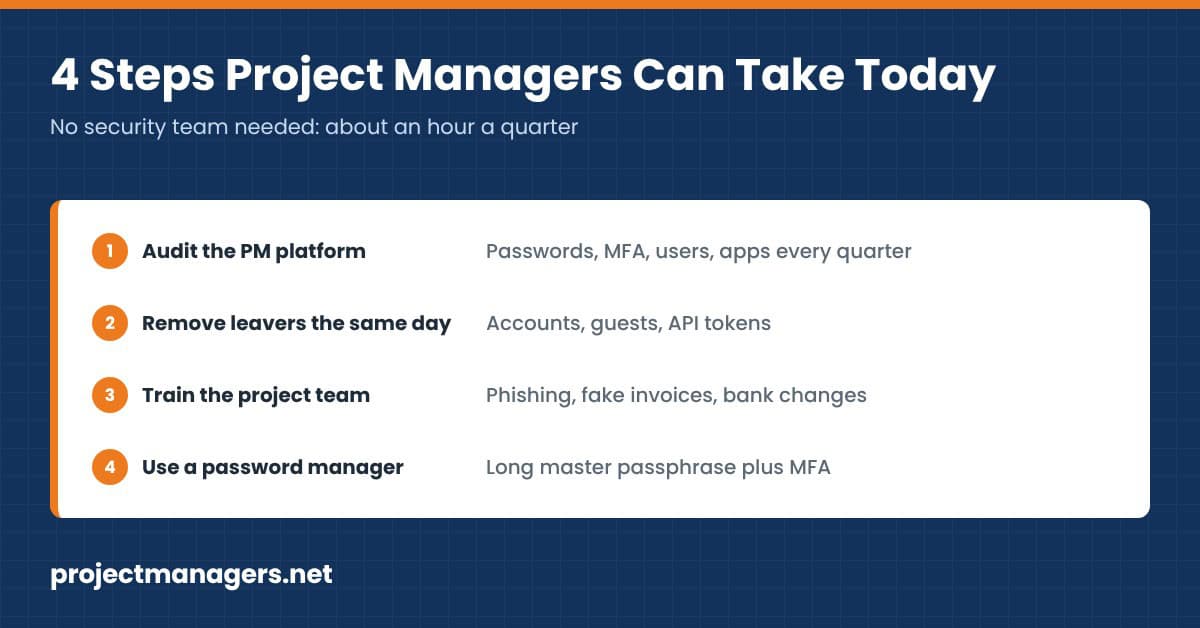
Beyond the security features built into your PM platform, a project manager controls a few habits that make a big difference. None of them need a security team, and most take less than an hour a quarter.
Audit Your PM Platform Every Quarter
Review your platform’s password rules, MFA settings, user list and connected apps at least once a quarter, and after any plan change. Write down what you find, assign each fix an owner and track it like any other project task. The free PM Platform Security Scorecard below gives you the checklist, a score and a fix list you can paste into your status report.
Remove Former Team Members the Same Day
Only current project team members should have access to your PM platform. When someone leaves the company or rolls off the project, remove their access the same day, including their API tokens and connected apps. Check guest and contractor accounts too: they are the ones most often forgotten after a project closes.
Real-life example
Cash App 2021: a former employee downloaded reports on 8.2 million customers
In December 2021, a former Block employee downloaded internal Cash App Investing reports that contained customer names and brokerage account numbers. The person had used these reports in their old job, but accessed them after their employment ended. Block found out four months later and contacted about 8.2 million current and former customers.
Source: TechCrunch, Block confirms Cash App breach after former employee accessed US customer data
For project managers: add “remove platform access” to every offboarding and project closeout checklist, with an owner and a same-day deadline. If your platform uses SSO, disabling the person’s company account removes access everywhere at once.
From the source
“these reports were accessed without permission after their employment ended”
Block, Inc., Form 8-K filed with the SEC
By the numbers
- 8.2Mcurrent and former customers were contacted about the incident.SEC filing
- 4 monthspassed between the download (December 2021) and the public disclosure (April 2022).TechCrunch
Educate Your Project Team
Preventing cyberattacks that start with human error means teaching team members good password habits and how to spot phishing. Cover long passphrases, why reuse is dangerous, fake login pages, urgent payment requests and changed bank details. The Center for Internet Security notes that 62% of breaches in the 2026 DBIR involved a human element, so a short session at your next team meeting is time well spent.
Agree on two simple rules: nobody shares a password in chat or email, and any request to change payment details is confirmed by phone with a known number. Then explain what to do after a suspected attack: who to call, what to lock and how to report it.
Use Password Managers the Right Way
Password managers create long random passwords, store them encrypted, fill them in for you and let the team share credentials safely. They remove the temptation to reuse a weak password across tools. But the vault is only as strong as its master password, so require a long passphrase plus MFA on the password manager itself.
Real-life example
LastPass 2022: encrypted vaults stolen, then cracked years later
In 2022, attackers stole backups of LastPass customer vaults. The vaults were encrypted, but anyone with a weak master password was exposed to offline guessing. Blockchain analysts at TRM Labs traced about $35 million in cryptocurrency drained from victims through 2025, much of it from people who never changed their master password after the breach.
Source: Infosecurity Magazine, Experts Trace $35m in Stolen Crypto to LastPass Breach
For project managers: a password manager is worth it, but set the rules: a passphrase of 15 characters or more, MFA on the vault and a forced master password change if the vendor reports a breach.
From the source
“Any vault protected by a weak master password could eventually be decrypted offline”
TRM Labs, quoted by Infosecurity Magazine
By the numbers
- ~$35Min crypto traced to cracked LastPass vaults through 2025.Infosecurity Magazine
- 3.2%of passwords leaked in 2025 had 16 characters or more.Comparitech
Free PM Platform Security Scorecard
Use the scorecard to check your own workspace in about five minutes. It opens with a typical free-plan setup so you can see how it works.
- Describe your platform: cloud or self-hosted, number of users and the most sensitive data it holds.
- Answer each control with Yes, Partly, No, Not sure or Not applicable. Check your admin settings when you are unsure.
- Read your score, the critical gaps and the fix list, sorted into Now, Next 30 days and Next quarter.
- Copy the summary for your status report, download the CSV for your risk register, print it, or send the vendor questions to your account manager.
PM Platform Security Scorecard
Rate how your project management platform handles passwords, MFA, access, encryption and updates. You get a score out of 100, the critical gaps, a fix list in priority order and the questions to send your vendor.
Summary copied
Runs in your browser. Nothing you enter is stored or sent. The score is a guide, not a security audit: confirm each answer in your platform’s admin settings or with the vendor.
The Role of Online Fraud Insurance

Even the strongest protections can be beaten by a convincing scam. Fake invoices, spoofed emails from a “supplier” and phishing links still get through, and when money leaves the account it is hard to get back. That is why online fraud insurance is worth considering as a last layer, after MFA, access controls and training. Depending on the policy, this type of coverage can:
- Reimburse money lost to phishing, email spoofing and fraudulent transfers
- Cover costs linked to identity theft, such as replacing documents and lost wages
- Give you access to experts who help you investigate and recover after an incident
- Support recovery after cyberattacks and cyber extortion
- Help with the practical and legal steps that follow a fraud
Read the policy carefully before you rely on it: check what is covered, the limits, the exclusions and who is eligible. Many consumer plans exclude scams aimed at a business, so a company may also need commercial cyber insurance. Insurance pays after the loss. It does not replace the controls that prevent it.
Real-life example
Orion 2024: an employee tricked into wiring about $60 million
In August 2024, chemical company Orion S.A. told the SEC that an employee, not a senior executive, had been the target of a criminal scheme that led to several fraudulent wire transfers. Orion expected a one-time charge of about $60 million and said it would pursue recovery, including through any available insurance coverage.
Source: Orion S.A., Form 8-K filed with the SEC
For project managers: if your project approves invoices or vendor payments, add a call-back step for any new or changed bank details, and know before an incident what your insurance does and does not cover.
From the source
“a one-time pre-tax charge of approximately $60 million”
Orion S.A., Form 8-K, August 2024
By the numbers
- $3.05Bin reported business email compromise losses in 2025.FBI IC3 2025 report
- $20.9Bin total cybercrime losses reported to the FBI in 2025.FBI IC3 2025 report
Protect Your Projects With Strong Security Practices
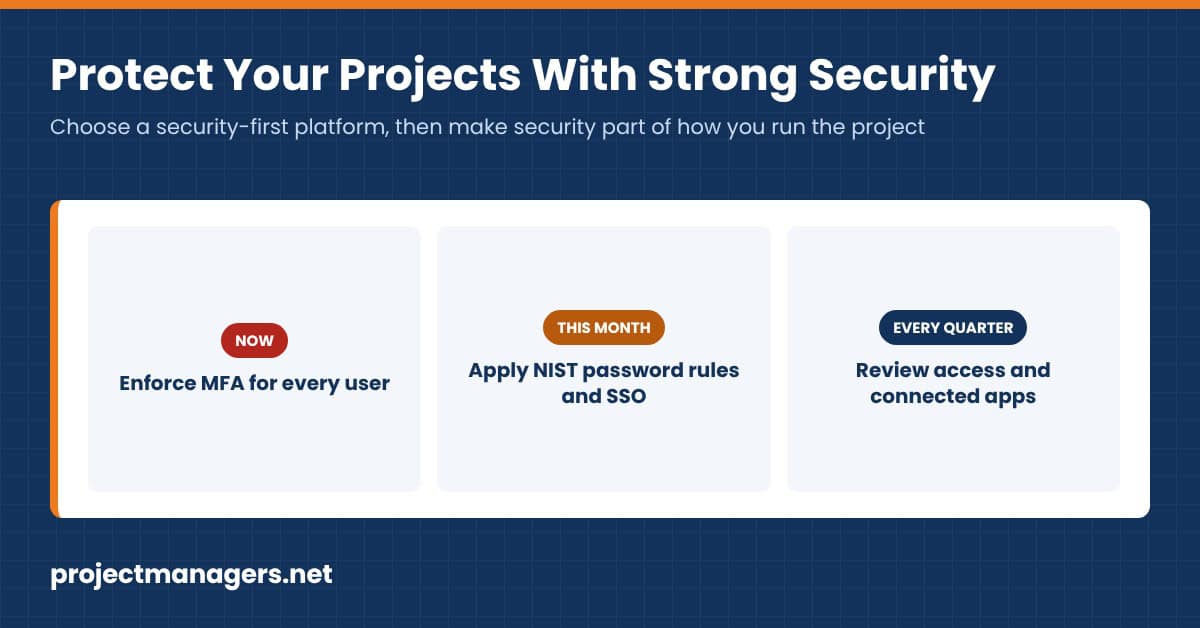
Weak, reused or personal-information passwords put every project in your workspace at risk. If your PM platform still accepts them, choose a security-first platform, or switch on the settings your current one already offers: enforced MFA, NIST-style password rules, SSO and role-based access.
Then make security part of how you run the project: review access every quarter, remove leavers the same day, train the team and keep fraud coverage in mind for what slips through. A breach now costs an average of $4.99 million worldwide according to IBM’s 2026 Cost of a Data Breach Report, far more than the hour a quarter it takes a project manager to stay ahead of it.
PM Platform Password Security Quiz
10 questions on PM platform password security
Check what you learned. Pick an answer, then open the explanation.
Of the 2 billion passwords leaked in 2025 that Comparitech studied, what share had fewer than 12 characters
- AAbout 15%
- BAbout 35%
- C65.8%
- D96.8%
Show answer
Answer C. Comparitech found 65.8% were under 12 characters, and only 3.2% had 16 or more.
According to NIST SP 800-63B-4, what is the minimum length for a password used as the only sign-in factor
- A8 characters
- B12 characters
- C15 characters
- D20 characters
Show answer
Answer C. NIST requires 15 characters when the password is the only factor and 8 when it is part of MFA.
Which password rule does NIST now say verifiers should NOT impose
- AChecking passwords against breach lists
- BForcing a mix of character types
- CAllowing at least 64 characters
- DForcing a change after a compromise
Show answer
Answer B. Composition rules such as forced symbols are out. Length and blocklist checks are in.
How did attackers get into Change Healthcare in February 2024
- AA zero-day in Citrix
- BStolen credentials on a portal without MFA
- CA malicious insider
- DA stolen laptop
Show answer
Answer B. UnitedHealth’s CEO testified that a Citrix remote access portal with stolen credentials did not have MFA.
Which MFA method resists phishing best
- ASMS codes
- BEmail codes
- CPasskeys or security keys
- DSecurity questions
Show answer
Answer C. Passkeys and FIDO2 security keys are bound to the real site, so a fake login page cannot reuse them.
In the 2024 Snowflake attacks, what was the main weakness
- AA bug in Snowflake’s platform
- BCustomer accounts with stolen passwords and no MFA
- CUnencrypted backups
- DA rogue Snowflake employee
Show answer
Answer B. Mandiant found the accounts used stolen credentials and did not have MFA enabled.
A contractor rolls off your project today. When should their PM platform access be removed
- AAt the next quarterly review
- BWhen the project closes
- CThe same day
- DWhen the client asks
Show answer
Answer C. Same-day removal closes the gap that let a former Cash App employee download customer reports.
What risk did the Asana MCP incident in 2025 show
- AWeak admin passwords
- BAn AI connector exposing data across organizations
- CA ransomware attack
- DA phishing campaign
Show answer
Answer B. A logic flaw in Asana’s MCP server could expose data from one organization to MCP users at others.
Why were some LastPass vaults stolen in 2022 cracked years later
- AThe vaults were not encrypted
- BTheir owners used weak master passwords
- CLastPass shared the keys
- DMFA codes were leaked
Show answer
Answer B. Encrypted vaults can be guessed offline when the master password is weak.
What does online fraud insurance do
- APrevents phishing emails
- BReplaces MFA
- CHelps recover losses after a covered fraud
- DPatches your PM platform
Show answer
Answer C. Insurance pays after a covered loss. It does not replace the controls that prevent it.
Video: How to Make Passwords More Secure
Jeff Crume of IBM explains in about three minutes why length beats complexity, why forced resets backfire and what the newer NIST guidance means for the password rules your project team uses.
Video by IBM Technology on YouTube: How to make passwords more secure
Facts Worth Checking
Each claim is checked against the original source.
| Claim | Verdict | What the source says |
|---|---|---|
| Most passwords leaked in 2025 were shorter than 12 characters. | True | Comparitech found 65.8% of the more than 2 billion passwords it studied had fewer than 12 characters. Comparitech |
| 38.6% of all passwords leaked in 2025 contained “123.” | Partly | The 38.6% figure applies to the 1,000 most common passwords in the data set, not to all 2 billion. Comparitech |
| Poor password habits caused 2.28 billion data leaks in the United States. | Partly | Demandsage counts 2.28 billion password-related leaks among 18.4 billion U.S. data points and names reuse as a possible reason, not a proven cause. Demandsage |
| CISA says MFA makes you 99% less likely to be hacked. | True | CISA’s multifactor authentication page states it directly. A Microsoft study measured a 99.22% lower risk of compromise. CISA |
| NIST still recommends forced symbols and password changes every 90 days. | False | SP 800-63B-4 forbids composition rules and scheduled changes, and requires a change only on evidence of compromise. NIST |
| Stolen credentials are still the top way into breaches. | False | In the 2026 DBIR, exploited vulnerabilities (31%) overtook credential abuse, though credential abuse still appears in 39% of attack chains. Center for Internet Security |
| Snowflake’s own platform was hacked in 2024. | False | Mandiant found attackers used stolen customer credentials on accounts without MFA. Snowflake’s systems were not breached. Mandiant |
| The Change Healthcare attackers got in with a stolen password and no MFA. | True | UnitedHealth’s CEO testified that a Citrix portal accessed with compromised credentials did not have MFA. TechCrunch |
| An encrypted password manager vault is safe even with a weak master password. | False | About $35 million was drained from users whose stolen LastPass vaults were cracked offline. Infosecurity Magazine |
| Business email compromise caused more than $3 billion in reported losses in 2025. | True | The FBI’s IC3 recorded 24,768 BEC complaints and $3.05 billion in losses in 2025. FBI IC3 |
Checked November 12, 2026.
Frequently Asked Questions
What makes a password weak?
A password is weak when it is short, common, based on personal information (names, birthdays, the company name) or reused on another site. Length is the biggest factor: NIST asks for at least 15 characters when the password is the only sign-in factor.
How long should a password be in 2026?
At least 15 characters when the password is used alone, and at least 8 when the account also uses MFA, according to NIST SP 800-63B-4. A passphrase of four or five random words is easy to remember and hard to guess.
Should we force users to change their passwords every 90 days?
No. NIST now says verifiers shall not require periodic changes, because people respond with small, predictable edits. Force a change only when there is evidence a password was exposed.
Is SMS-based MFA good enough for a PM platform?
It is much better than a password alone, but SMS codes can be phished or intercepted. Use passkeys, security keys or an authenticator app for admins and anyone who approves payments, and keep SMS as a fallback.
How often should a project manager audit PM platform access?
At least once a quarter, plus after any plan change, team change or project closeout. Export the user list, remove inactive and unknown accounts, check admin rights and review connected apps.
What should I do when a team member leaves the project?
Remove their access the same day, including guest accounts, API tokens and connected apps, and change any shared passwords they knew. With SSO, disabling the company account removes access to every connected tool at once.
Does online fraud insurance replace good security?
No. Insurance helps you recover money and costs after a covered fraud, within the policy limits and exclusions. MFA, access controls, training and payment call-backs are what prevent the loss in the first place.
Suggested articles:
- Preventing Ransomware and Cyber Extortion in Project Teams
- Managing AI-Specific Cybersecurity Risks in Project Planning and Execution
- Top 10 Pros and Cons of Penetration Testing Services for Project-Driven Businesses
- Best Third-Party Risk Management Tools for Small Businesses
- Free Risk Register Templates

Daniel Raymond, a project manager with over 20 years of experience, is the former CEO of a successful software company called Websystems. With a strong background in managing complex projects, he applied his expertise to develop AceProject.com and Bridge24.com, innovative project management tools designed to streamline processes and improve productivity. Throughout his career, Daniel has consistently demonstrated a commitment to excellence and a passion for empowering teams to achieve their goals.