

The sheer volume of data in today’s world has led to an enormous increase in the complexity of the systems used in modern marketing. Marketing relies on many different technologies, from customer relationship management (CRM) systems to data analytics systems, marketing automation systems, and customer data platforms (CDP). APIs (Application Programming Interfaces) allow these different components of a marketing technology stack to communicate. With the use of APIs, marketing technologies can be highly efficient and easily scalable. However, APIs also introduce several security risks that every project manager needs to plan for.
- Every API in a marketing stack moves customer data, so each integration is a security risk point the project manager must track.
- Broken authentication, excessive data exposure, missing rate limits, injection attacks, and misconfigured endpoints are the most common API risks.
- Build API security into every project phase: map data flows in planning, validate integrations in execution, and monitor after launch.
- Project managers do not need to be security experts, but they must assign clear owners, balance risk with deadlines, and test before go-live.
For project managers, understanding the risks associated with API security should be a priority. This guide describes the many different ways that API security can impact a marketing technology stack, and also describes ways in which project managers can mitigate those risks.
APIs in Marketing Technology

In modern marketing operations, APIs are present in the vast majority of systems that marketing teams use. APIs enable the secure exchange of data and communication between platforms, which makes campaign personalization, targeting, and operational efficiency possible. Real-time API connections help marketers deliver timely, relevant experiences at scale.
Role of APIs in Martech Ecosystems
APIs are ubiquitous in modern marketing technology. Marketing technology makes use of APIs to link and connect customer relationship management (CRM) tools, email marketing software, analytics systems, and advertising platforms.
For example, an API may be used to send data from a marketing automation tool to a customer relationship management tool (CRM), trigger an email automation tool, and update an analytics dashboard. Such a system may be quite complex, and it also has several security vulnerabilities associated with it.
Why APIs Are a Growing Target
Attackers target APIs because they reveal critical business components and data. APIs can also be very insecure. Many traditional web applications’ APIs may not have thorough documentation and security controls. Weak authentication, unscrutinized endpoint security, and uncontrolled data streams are, in fact, common attack vectors.
This is of utmost importance for project and product managers, as marketing stack integrations need preemptive security assessments in addition to functional evaluations before they are plugged into the existing systems.
The Importance of API Security in Marketing Projects
API security plays a critical role in protecting sensitive customer data and ensuring the integrity of marketing operations.
Protecting Customer Data
Marketing systems handle sensitive personally identifiable information (PII) such as names, emails, phone numbers, and behavioral insights. If an API is compromised, attackers can extract this data at scale, leading to legal exposure, regulatory penalties, and long-term damage to customer trust and brand credibility.
Ensuring Campaign Integrity
APIs control how data moves across marketing tools, from CRMs to automation platforms. If compromised, attackers can manipulate campaign logic, alter targeting parameters, inject malicious content, or disrupt workflows, resulting in inaccurate reporting, wasted budgets, and reputational harm across multiple marketing channels.
Maintaining Compliance
Data protection laws like GDPR require strict control over how customer data is accessed, processed, and stored. Vulnerable APIs can bypass these safeguards, exposing organizations to compliance violations, heavy fines, legal scrutiny, and loss of operational credibility in regulated markets and industries.
Supporting Business Continuity
A single API breach can disrupt entire marketing operations by breaking integrations, halting campaigns, or corrupting data pipelines. Strong API security ensures systems remain stable, campaigns run without interruption, and revenue streams are protected from unexpected downtime or malicious interference.
Common API Security Risks in Marketing Tech Stacks
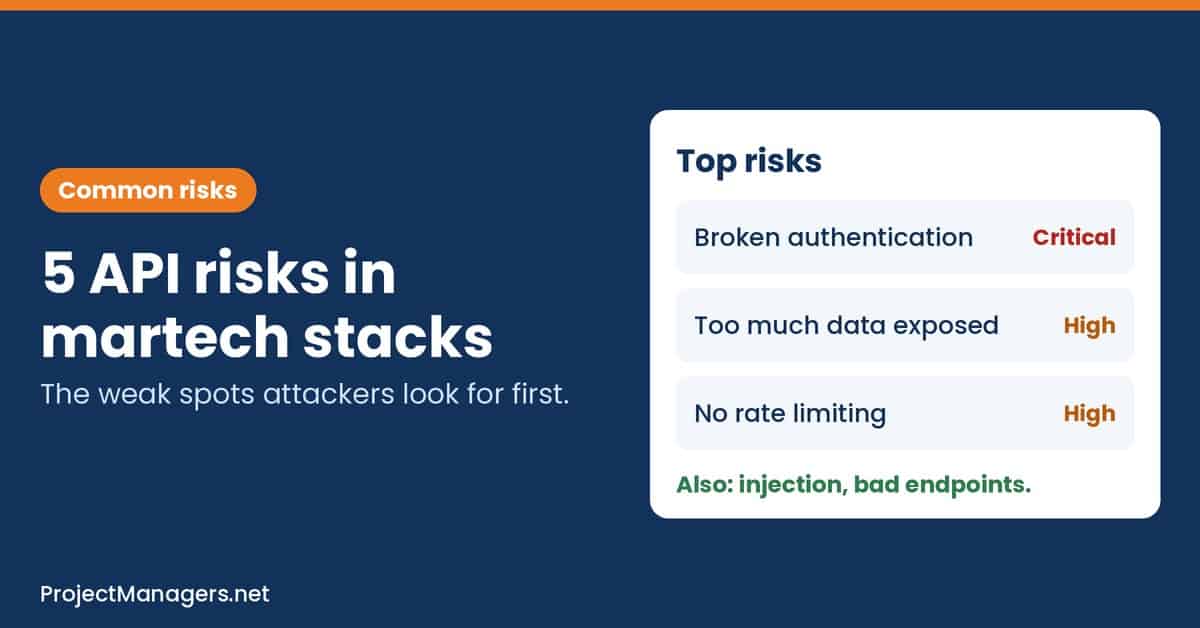
Understanding the types of vulnerabilities that can occur in APIs is essential for effective risk management in every marketing project.
Broken Authentication and Authorization
Weak authentication allows attackers to impersonate users, while poor authorization grants access beyond intended permissions. This combination can expose sensitive data and critical functions, making it easy for attackers to move laterally across systems and gain deeper control over marketing infrastructure.
Excessive Data Exposure
APIs often return more data than necessary, especially when poorly configured. This overexposure gives attackers access to sensitive fields that should remain hidden, increasing the risk of data leaks and making it easier to piece together valuable information for exploitation.
Lack of Rate Limiting
Without rate limiting, APIs become vulnerable to abuse through repeated automated requests. Attackers can launch brute-force attacks, overwhelm systems with traffic, or scrape large volumes of data, leading to degraded performance, service outages, and potential system failures.
Injection Attacks
APIs that fail to properly validate user input are vulnerable to injection attacks such as SQL or command injections. These attacks allow malicious code execution, enabling attackers to access, modify, or delete backend data and potentially take control of entire systems.
Misconfigured Endpoints
Improperly configured APIs can unintentionally expose hidden endpoints, debugging data, or administrative functions. These weaknesses provide attackers with direct entry points into sensitive areas of the system, often without triggering alerts, making them especially dangerous and difficult to detect.
Key API Security Components for Project Managers

Project managers do not need to be cybersecurity experts, but they must understand the core components of API security to effectively manage risks.
Authentication and Access Control
Secure APIs use strong authentication methods such as OAuth tokens, API keys, or multi-factor authentication. Access control ensures that users and systems only have permissions relevant to their roles. For project managers overseeing complex martech integrations, building this layer from scratch is rarely the right call.
Identity management platforms such as Auth0 offer pre-built OAuth 2.0 and OpenID Connect flows, role-based access control, and anomaly detection out of the box, reducing both implementation time and the risk of misconfiguration. For teams managing software budgets, JoinSecret is worth bookmarking. It centralizes exclusive deals and promo codes on tools like Auth0 and many of the other SaaS platforms commonly used in martech stacks.
This is particularly valuable in marketing stacks where multiple third-party tools (ad platforms, CDPs, email systems) each require their own authentication handshakes. Centralizing identity management through a dedicated solution ensures that access policies remain consistent across the entire ecosystem, even as integrations evolve.
Encryption and Data Protection
APIs must encrypt data in transit using protocols like HTTPS to prevent interception. Without encryption, sensitive customer and campaign data can be captured during transfer. Proper data protection also includes securing stored data and ensuring only authorized systems can decrypt and process it.
Monitoring and Logging
Continuous monitoring tracks API activity in real time, helping detect unusual patterns such as repeated failed requests or abnormal data access. Logging creates a record of all interactions, enabling faster investigations, compliance reporting, and quicker response to potential breaches or misuse.
Testing and Validation
Regular API testing identifies vulnerabilities before attackers do. This includes automated scans, penetration testing, and validation of input handling. Consistent testing ensures APIs remain secure as systems evolve, integrations expand, and new features are introduced into the marketing technology stack.
Selecting the Right API Testing Tools for Your Martech Stack
Not all testing solutions are built with marketing infrastructure in mind. Traditional security scanners often struggle with the dynamic, token-based authentication flows common in CRM, automation, and analytics APIs. Purpose-built automated pentesting tools designed for web and API environments go further: they map business logic, simulate real attack chains, and produce actionable reports that project managers, not just security engineers, can interpret and prioritize.
When evaluating options, look for tools that integrate into your CI/CD pipeline, support REST and GraphQL endpoints, and flag issues like broken object-level authorization (BOLA), which is among the most exploited vulnerabilities in martech APIs.
Integrating API Security into Project Management

API security should be embedded into every phase of a marketing project lifecycle rather than treated as an afterthought.
Planning Phase
During planning, project managers must identify all APIs involved and map how data flows between systems. This step helps uncover potential vulnerabilities early, define security requirements, and ensure that risk assessments are built into the project before any development or integration begins.
Execution Phase
In execution, teams must enforce secure coding practices, validate all API integrations, and implement proper authentication measures. Security should be actively monitored during development, ensuring that vulnerabilities are addressed immediately rather than postponed until after deployment. This matters most for integrations that trigger real-world actions. When a team connects a direct mail api to the CRM so postcards and letters go out on lifecycle events, a faulty call or a bad data mapping can put the wrong message in thousands of mailboxes. Postalytics, for example, offers mock and development environments so developers can validate workflows before a real print job is triggered, which gives the project manager a clear checkpoint to sign off on before go-live.
Monitoring Phase
Once deployed, APIs require continuous oversight to detect threats in real time. Monitoring tools should track usage patterns, flag anomalies, and alert teams to suspicious behavior. This ensures that potential attacks are identified early before they escalate into major security incidents.
Review and Optimization
Post-launch reviews allow teams to assess API performance and security effectiveness. By analyzing past vulnerabilities and incidents, project managers can refine processes, strengthen defenses, and apply lessons learned to future campaigns and system integrations for continuous improvement.
API Security Tools and Technologies
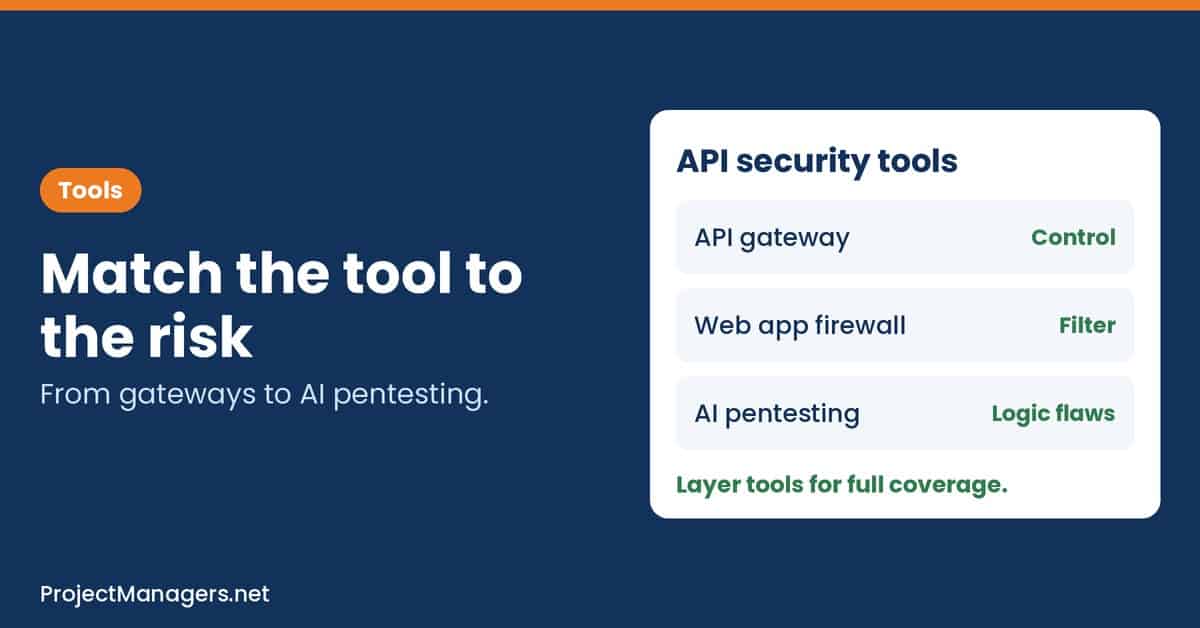
Various tools are available to help secure APIs within marketing tech stacks. These tools range from testing platforms to monitoring solutions.
Traditional API Security Tools
Traditional tools like API gateways, firewalls, and scanners provide foundational protection by controlling access, filtering traffic, and identifying known threats. While effective for baseline security, they often lack the depth needed to detect complex vulnerabilities in modern, highly dynamic marketing systems.
AI-Powered Security Solutions
AI-driven tools analyze large volumes of API traffic to detect unusual behavior and hidden vulnerabilities. They can identify patterns that traditional tools miss, enabling faster threat detection, automated responses, and deeper insights into complex attack methods targeting marketing technology environments.
Comparison of API Security Tools
API Security Tools Compared
Five tool types, what each one does, and where it helps a marketing project.
| Tool Type | Primary Function | Key Benefit | Use Case in Marketing Projects |
|---|---|---|---|
| API Gateway | Manages API traffic and access | Centralized control | Securing multiple marketing integrations |
| Web Application Firewall | Filters malicious traffic | Real-time threat protection | Protecting customer-facing APIs |
| Security Testing Tools | Identifies vulnerabilities | Early risk detection | Pre-launch testing of campaigns |
| Monitoring & Analytics Tools | Tracks API activity | Continuous visibility | Detecting anomalies in live campaigns |
| AI Penetration Testing Tools | Simulates advanced attack scenarios | Deep vulnerability detection | Identifying complex business logic flaws |
The Role of Project Managers in API Security
Project managers play a crucial role in ensuring that API security is prioritized throughout marketing projects.
Bridging Technical and Business Teams
Project managers act as a link between developers, security teams, and marketing stakeholders. They ensure developers, marketers, and stakeholders stay aligned, preventing gaps in understanding that can lead to vulnerabilities. This coordination is critical in maintaining both system security and project efficiency.
Risk Management and Decision-Making
By understanding API risks, project managers can prioritize security alongside deadlines and budgets. They make informed trade-offs, allocate resources effectively, and ensure high-risk areas receive attention, reducing the likelihood of costly breaches or disruptions later in the project lifecycle.
Ensuring Accountability
Project managers enforce security standards by holding teams responsible for following best practices. They ensure clear ownership of API security tasks, track compliance, and prevent gaps where responsibilities are unclear, which is often where vulnerabilities slip through unnoticed.
Challenges in Securing Marketing APIs
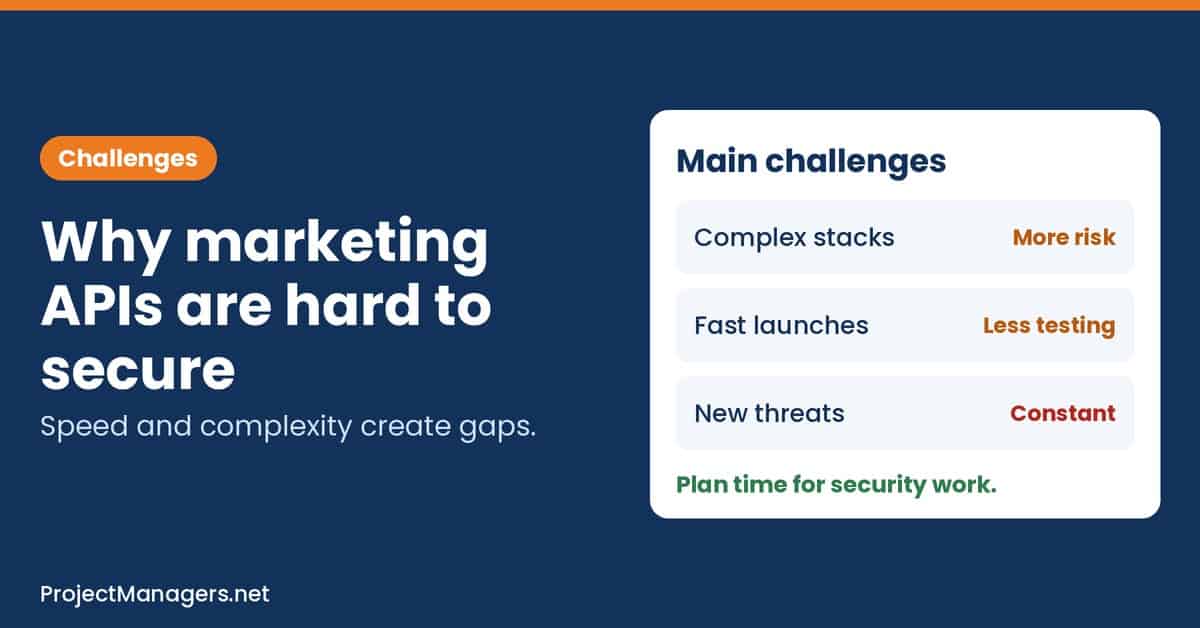
Despite its importance, API security presents several challenges for every marketing project team.
Complexity of Martech Stacks
Modern marketing stacks combine multiple platforms, integrations, and data flows, making them difficult to secure. Each connection introduces a new risk point, and without clear visibility, vulnerabilities can remain hidden across interconnected systems.
Rapid Deployment Cycles
Marketing teams often prioritize speed to launch campaigns quickly, which can lead to security shortcuts. Tight timelines reduce time for proper testing and validation, increasing the likelihood of overlooked vulnerabilities that attackers can exploit once systems go live.
Evolving Threat Landscape
Cyber threats are constantly changing, with attackers developing new methods to exploit APIs. Static security measures quickly become outdated, requiring continuous updates, monitoring, and adaptation to defend against increasingly sophisticated and targeted attacks.
Future Trends in API Security for Marketing

The future of API security is closely tied to advancements in technology and the growing complexity of digital ecosystems.
Increased Adoption of AI
AI will increasingly automate threat detection, analyze behavior patterns, and respond to incidents faster than manual processes. This reduces response times and improves accuracy, making it a critical component in managing API security within complex marketing ecosystems.
Shift Toward Zero-Trust Architecture
Zero-trust security models require every API request to be verified, regardless of its origin. This eliminates implicit trust within systems, reducing the risk of internal breaches and ensuring stricter access control across all marketing tools and integrations.
Greater Emphasis on Compliance
As data privacy regulations tighten globally, organizations must strengthen API security to remain compliant. This includes stricter data handling, improved audit trails, and proactive risk management to avoid penalties and maintain trust with customers and partners.
API Security Checklist for Marketing Projects
Use this checklist at each project gate, from kickoff to go-live, to confirm the API security work is done and has an owner:
- Inventory: Every API and third-party integration in the project is listed, with the data each one sends and receives.
- Data Flow Map: The team has mapped how customer data moves between the CRM, automation, email, analytics, and ad platforms.
- Access: Each integration uses strong authentication, and users and systems only have the permissions their role needs.
- Encryption: All API traffic uses HTTPS, and stored customer data is protected.
- Data Minimization: APIs return only the fields each tool actually needs.
- Rate Limits and Monitoring: Rate limits are set, and alerts flag unusual activity such as repeated failed requests.
- Testing: Integrations are tested in a sandbox or development environment before any live campaign or real-world action is triggered.
- Ownership: Every security task has a named owner, and a post-launch review is scheduled in the project plan.
If a box cannot be checked, add the gap to the project risk register with an owner and a due date before the next milestone.
Video: Top Tips for API Security
Prefer to watch? This short video covers practical API security habits, from HTTPS and OAuth to rate limiting and input validation, that project managers can turn into requirements for their teams.
Top 12 Tips for API Security (ByteByteGo, 9:47)
An April 2024 explainer of twelve proven ways to secure an API, a handy reference when the project team writes its security requirements.
API Security in Marketing Projects FAQ
API security for project managers: FAQ
Why should project managers care about API security?
Because every API in a marketing stack moves customer data between tools. A single weak integration can leak personal data, break campaigns, or create compliance problems, which turns a technical issue into a project delay, a budget overrun, and a reputational risk.
Do project managers need to be security experts?
No. Project managers need to understand the core risks and controls well enough to ask the right questions, add security tasks to the project plan, assign owners, and make sure testing happens before go-live.
What are the most common API security risks in martech stacks?
Broken authentication and authorization, excessive data exposure, lack of rate limiting, injection attacks, and misconfigured endpoints. Broken object-level authorization (BOLA) is among the most exploited issues in martech APIs.
When should API security be planned in a marketing project?
From the planning phase. Identify every API and map data flows before development starts, then validate integrations during execution, monitor them after launch, and review results at the end of each project.
How can a project team test an API integration safely?
Use a sandbox, mock, or development environment so the team can validate workflows, data mapping, and error handling before a live campaign or real-world action, such as a print job or an email send, is triggered.
What tools help secure marketing APIs?
API gateways centralize access control, web application firewalls filter malicious traffic, security testing tools find vulnerabilities before launch, monitoring tools track live activity, and AI penetration testing tools uncover complex business logic flaws.
How does API security support GDPR compliance?
GDPR requires strict control over how customer data is accessed, processed, and stored. Secure APIs with strong authentication, encryption, data minimization, and audit logs help a project prove that personal data is protected.
Conclusion
Risk mitigation is as important as API integration and automation tools in marketing technology. Project managers are tasked with ensuring security by design throughout the project life cycle and in every element of the project. By understanding API vulnerabilities, leveraging the right tools, and fostering collaboration between teams, project managers can ensure that marketing initiatives are not only effective but also secure. In an era where data is one of the most valuable assets, securing APIs is not just a technical requirement; it is a strategic necessity.
Author Details
Ombir Sharma is the Managing Partner at Tecuy Media, leveraging extensive experience in digital marketing to drive business growth. He also leads LinksFrog, a company specializing in high-quality SaaS backlinks and strategic link-building to enhance website rankings and organic traffic. With a strong foundation in SEO, content strategy, keyword research, and analytics, Ombir excels at crafting engaging, optimized content and implementing innovative SEO strategies that deliver measurable results. His passion for staying ahead of industry trends allows him to blend creativity with data-driven strategies, creating impactful online experiences that fuel success.
Suggested articles:
- Google Calendar API Integration: Best Practices, Security, and a Faster Path with Unipile
- How Open Banking APIs Can Help Project Managers
- Top Benefits of Using Node.js to Fetch APIs

ProjectManagers.net is a website that provides articles about project management software, training, templates, and resources tailored for project managers. Enhance skills and streamline workflows.